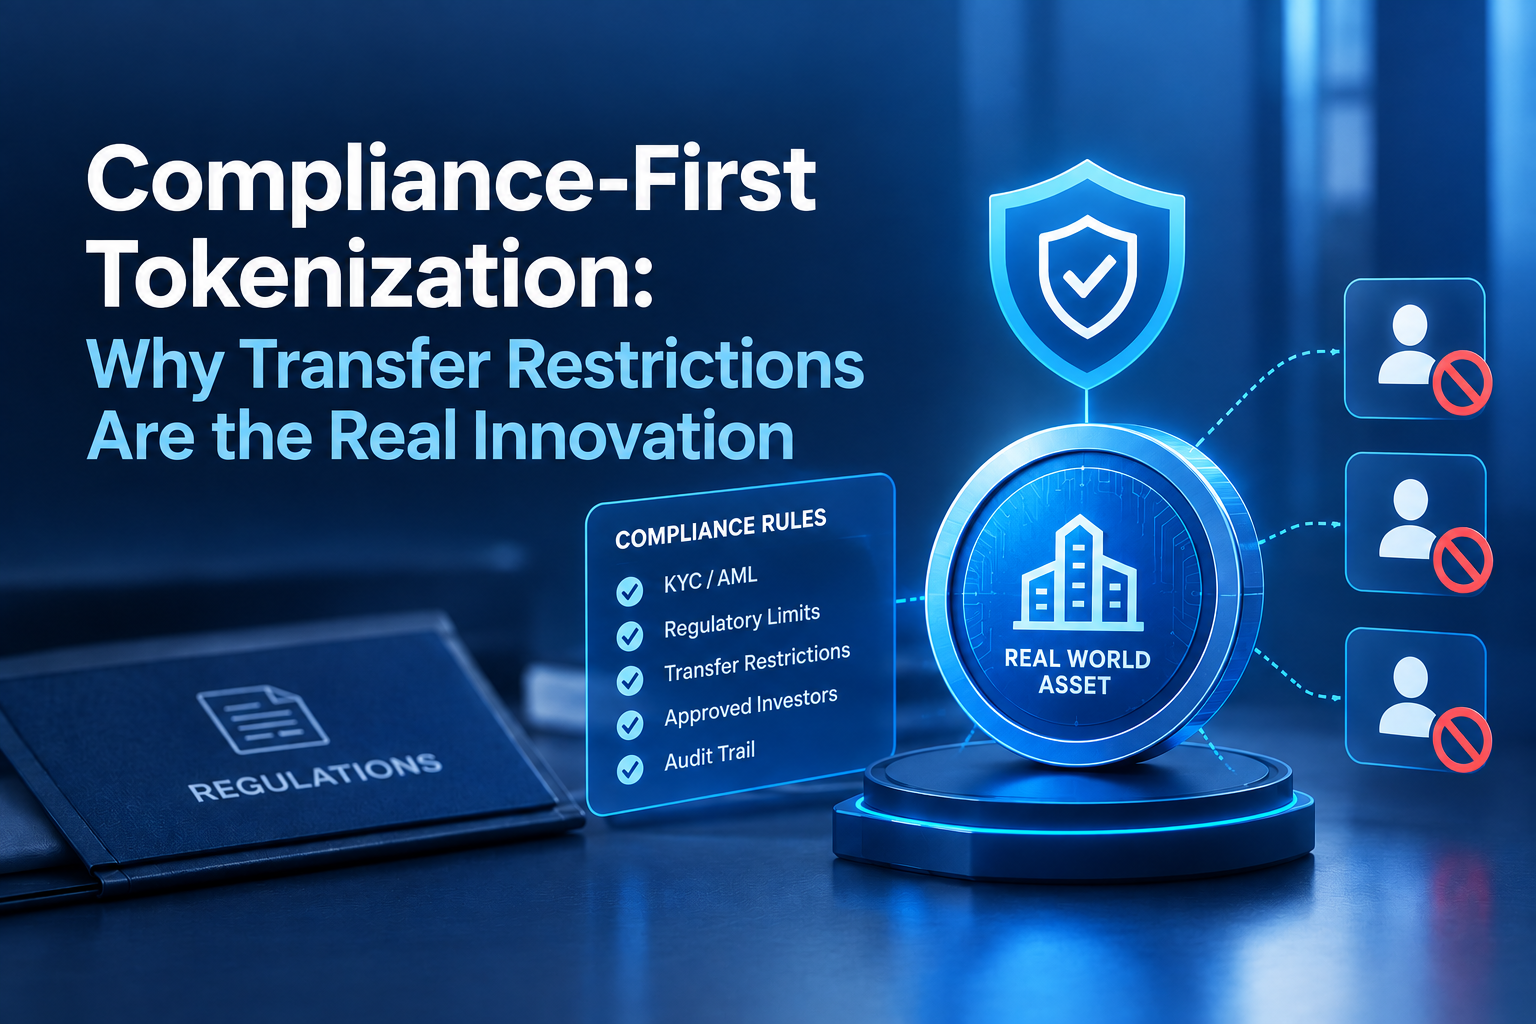
Ask most people what makes asset tokenization innovative, and they'll describe putting a bond, a property, or a fund interest "on-chain." That's the part that gets the headlines. It's also, from an institutional standpoint, the easy part.
Creating a digital token that represents an asset is a solved problem. Enforcing who is allowed to hold that token, receive it, transfer it, or redeem it—under the correct regulatory, jurisdictional, and contractual conditions—is not. That enforcement layer is where compliance-first tokenization earns its name, and it's where most real institutional value actually sits.
For banks, asset managers, issuers, and fintech infrastructure teams evaluating tokenization, this distinction changes the entire evaluation. The question isn't "can we create a token for this asset?" It's "can this token only move between eligible parties every time, without relying on someone remembering to check?" That second question is what transfer restrictions are built to answer.
A blockchain record of ownership is not, by itself, a compliant financial instrument. Recording that Wallet A holds 500 units of a token tells you nothing about whether Wallet A belongs to a KYC-verified investor, whether that investor is legally permitted to hold the asset, or whether a proposed transfer to Wallet B would violate a jurisdictional restriction, a lock-up period, or an ownership cap.
This is the gap between token creation and compliant token infrastructure. Token creation is a technical exercise: mint a representation of an asset, assign it an identifier, put it on a ledger. Compliant token infrastructure is an operational and legal exercise: define who can participate, encode the conditions under which participation is allowed, and make sure every transfer is checked against those conditions before it settles.
Institutional adoption depends on the second definition. A pension fund, a broker-dealer, or a regulated issuer cannot treat a token the way a public blockchain treats a cryptocurrency — freely transferable to any address, by design. Regulated assets require controls around who can hold, receive, transfer, and redeem the token, applied consistently and provably, for the life of the asset.
Transfer restrictions are the rules that govern whether a specific token transfer is allowed to happen. In traditional finance, these rules already exist — they live in subscription agreements, transfer agent procedures, prospectus terms, and compliance manuals. Compliance-first tokenization doesn't invent new rules; it gives existing rules a mechanism to be checked automatically, consistently, and at the moment a transfer is attempted.
Common categories of transfer restrictions include:
A simple way to picture this: imagine a tokenized private fund interest that can only be held by accredited investors in specific countries, with a 12-month lock-up. Without transfer restrictions, that token is just a bearer instrument—whichever holds the private key controls the asset, regardless of eligibility. With transfer restrictions in place, an attempted transfer to an ineligible wallet simply fails, the same way a transfer agent would reject a non-compliant trade today.
It helps to compare two models of tokenization directly.
Traditional tokenization approach: Asset → Token → Wallet → Transfer
Compliance-first model: Asset → Eligibility → Compliance Rules → Token Issuance → Controlled Transfer → Settlement → Reporting
The first model treats compliance as something that happens before or after tokenization—a gate at onboarding, followed by unrestricted movement. It's simple, but it assumes every future holder was already vetted at some earlier point, which rarely holds true once a token can move peer-to-peer.
The second model treats compliance as continuous. Eligibility is established, rules are attached to the asset itself, and every transfer — not just the initial issuance — is evaluated against those rules. Settlement only occurs once a transfer is approved, and the activity is logged for reporting and audit purposes.
For regulated financial assets, the second model isn't an enhancement—it's closer to a requirement. Securities laws, fund documents, and AML obligations don't stop applying after issuance; they apply to every subsequent transfer for the life of the instrument. A tokenization approach that only checks compliance once creates a compliance gap the moment the token changes hands.
This is the core idea behind compliance by design: rules are associated directly with the asset or token, so that compliance conditions are evaluated automatically before a transfer is allowed to complete, rather than being checked manually after the fact.
In practice, this plays out across a spectrum:
It's worth being direct about the limits here: not every regulatory requirement can or should be fully automated. Suitability assessments, beneficial ownership determinations, and many AML judgment calls still require human review and legal interpretation. Compliance-first tokenization doesn't replace that judgment — it ensures that once a determination is made, it's consistently enforced at the infrastructure layer instead of depending on manual checks at every subsequent transfer.
Consider a tokenized private-market asset — for example, a tranche of a corporate bond offered to institutional investors in a defined set of jurisdictions.
If a transfer violates a rule—say, the receiving wallet hasn't completed KYC, or the sale would breach a lock-up period — the transaction is rejected before settlement. No ownership change occurs, and the attempted transfer is logged, giving compliance and legal teams a record of what was attempted and why it failed. This is a meaningful shift from many manual processes, where a non-compliant transfer might only be caught after the fact, during an audit or reconciliation.
This comparison isn't a case for removing human oversight—it's a case for removing repetitive manual checks from routine transfers so compliance teams can focus on genuine exceptions, policy design, and regulatory judgment calls.
A wallet address, on its own, is not a legally recognized owner. It's a cryptographic identifier. For regulated tokenized assets, the wallet has to be linked to a verified identity before it can meaningfully participate in the asset's lifecycle.
This is why compliance-first tokenization treats identity as foundational infrastructure, not an add-on:
The distinction that matters here is between blockchain address ownership and legally recognized ownership. A private key controls what happens to tokens at an address, but it doesn't, by itself, establish who is legally entitled to hold that asset under securities law or the offering's terms. Compliance-first tokenization closes that gap by requiring the two to be linked — and by making that link a precondition for any transfer, not a one-time onboarding formality.
Regulatory requirements for the same underlying asset can vary significantly depending on:
Consider a cross-border example: a real estate fund based in one jurisdiction tokenizes fractional interests and offers them to investors in several countries. An investor in one jurisdiction might qualify to hold the token under a private placement exemption, while an investor in another jurisdiction might be excluded entirely unless the offering is registered there, or might face different disclosure and holding-period requirements.
A compliance-first architecture allows these differences to be encoded as rules tied to the token itself — so a transfer to an investor in an excluded jurisdiction is blocked automatically, regardless of whether that investor would otherwise appear "eligible" on other criteria. Importantly, these rules have to be configurable and updatable, since regulatory frameworks and offering terms change over time; a static, hardcoded rule set becomes a liability rather than a safeguard.
It's worth noting explicitly: securities regulations, investor protections, and offering rules differ by country and by asset type, and none of the frameworks discussed here should be read as universal. What qualifies as an eligible investor, an exempt offering, or an acceptable holding period varies by jurisdiction and by the legal structure of the specific offering.
Permissioned, or controlled-access, blockchain infrastructure is often a natural fit for compliance-first tokenization, though it's not a compliance guarantee on its own.
Permissioned networks support:
None of this means a permissioned network is automatically compliant. Compliance still depends on the rules configured within that infrastructure — the KYC/AML processes, the eligibility logic, the transfer restriction rules — being correctly designed and maintained. Permissioned infrastructure creates the conditions under which compliance-first design is practical to implement; it doesn't substitute for that design.
Secondary trading is where the tension between liquidity and compliance becomes most visible. Tokenization is often pitched on its ability to unlock liquidity for traditionally illiquid assets — but liquidity without controls just recreates the compliance risks of an unregistered, unrestricted security.
Relevant considerations for secondary markets include:
The practical resolution most institutions land on is not unrestricted secondary trading, but controlled liquidity: a secondary market that exists within the same eligibility and jurisdictional rules that governed the primary offering, enforced automatically rather than relying on each counterparty to self-police.
At a high level, compliance-first tokenization infrastructure tends to include these layers, working together:
These layers interact continuously rather than sequentially. A transfer request doesn't just move through the blockchain layer — it's evaluated by the compliance rules engine against current identity and eligibility data before the blockchain layer is ever asked to record anything. The reporting layer then captures the full decision trail, regardless of whether the transfer was approved or rejected.
Tokenized private credit. Transfer restrictions ensure that debt instruments only circulate among investors who meet the terms of the original credit agreement, and that lock-up or amortization schedules are respected through the life of the loan.
Tokenized corporate bonds. Bondholders typically need to meet specific investor classification requirements; transfer restrictions prevent a bond from ending up with an ineligible holder through secondary transfer, which could jeopardize the offering's exemption status.
Tokenized real estate. Fractional property interests often carry jurisdiction-specific restrictions and holding-period requirements tied to how the offering was structured; enforcing these at the token level prevents fractional ownership from drifting outside the terms investors originally agreed to.
Tokenized funds. Fund interests frequently require investor accreditation and may include lock-up periods tied to redemption windows; programmable transfer rules keep secondary activity aligned with the fund's governing documents.
Tokenized commodities. Depending on structure, commodity-backed tokens may carry restrictions tied to custody arrangements or regional regulatory treatment, making eligibility checks relevant even for physically-backed assets.
Private-market securities generally. Across private placements, transfer restrictions are often the mechanism by which an offering maintains its exemption from full public registration — making them not just a risk-management feature but a legal necessity.
In each case, the common thread is the same: the value of tokenization is undermined if the token can end up in the hands of an ineligible holder, however efficient the initial issuance process was.
Before selecting infrastructure for institutional asset tokenization, enterprise teams — compliance, legal, and technology leaders together — should work through a practical checklist:
A platform that scores well on token creation but poorly on this checklist is solving the easier half of the problem.
The next stage of this evolution looks less like "assets on a blockchain" and more like assets that carry machine-readable rules governing who can hold them, who they can be transferred to, where they're allowed to move, when transfers are permitted, and under what conditions they can be redeemed or settled.
This is a meaningful shift in how compliance is operationalized — but it's worth being precise about what it does and doesn't replace. Machine-readable rules can enforce a determination consistently once it's been made. They don't replace the legal interpretation required to make that determination, the regulatory oversight that governs the asset, or the institutional governance processes that decide what the rules should be in the first place. Policy-aware assets are a way of executing compliance decisions reliably at scale — not a substitute for the judgment behind those decisions.
The most consequential part of institutional tokenization isn't the token. It's the infrastructure that determines who can hold that token, under what conditions it can move, and how those conditions are enforced consistently across the asset's entire lifecycle.
Transfer restrictions are where that infrastructure does its real work — turning compliance from a periodic, external check into a property of the asset itself. For banks, asset managers, issuers, and fintech teams evaluating tokenization platforms, this is the layer worth scrutinizing most closely, because it's the layer that determines whether a tokenized asset is actually usable within a regulated environment.
Platforms built with this problem in mind — Spydra among them — approach tokenization as more than digitization: configurable compliance rules, identity-linked wallets, jurisdiction-aware transfer logic, and audit-ready reporting built into the asset lifecycle from issuance through secondary transfer and redemption. The specifics of any given implementation still depend on the asset, the jurisdiction, and the offering structure — but the underlying principle holds across all of them: compliant infrastructure, not token creation, is where institutional tokenization is won or lost.
What is compliance-first tokenization?
Compliance-first tokenization is an approach to asset tokenization where eligibility, regulatory, and transfer rules are built directly into the token's infrastructure, so that every transfer — not just the initial issuance — is automatically checked against those rules before it can settle.
How are transfer restrictions different from KYC?
KYC verifies who an investor is. Transfer restrictions determine whether a specific proposed transfer is allowed to happen, based on eligibility, jurisdiction, lock-up periods, ownership limits, and other rules — often using KYC status as one input among several.
Can compliance be fully automated in tokenized securities?
Not entirely. Automated systems can consistently enforce rules once a legal or regulatory determination has been made, but interpreting regulations, assessing suitability, and making beneficial ownership determinations typically still require human and legal judgment.
Do transfer restrictions limit liquidity?
They shape liquidity rather than eliminate it. Transfer restrictions can limit who a token can be sold to, but they allow institutions to offer secondary liquidity within a compliant, controlled pool of eligible investors rather than choosing between full illiquidity and unrestricted, non-compliant transferability.
Is permissioned blockchain required for compliant tokenization?
No single architecture is required. Permissioned infrastructure often makes it easier to implement identity-linked access and governance controls, but compliance ultimately depends on how eligibility and transfer rules are designed and enforced, not on the underlying network type alone.
How do jurisdiction-based transfer rules work in tokenization?
Jurisdiction-based rules restrict or modify how a token can be transferred depending on the investor's location, the issuer's location, and the applicable securities regulations for each relevant jurisdiction. These rules need to be configurable, since requirements vary by country and by offering.
What happens if a token transfer violates a compliance rule?
The transfer is typically rejected before settlement, meaning ownership does not change. The attempted transfer is usually logged for audit purposes, giving compliance teams visibility into what was attempted and why it failed.
Why do institutions care more about transfer restrictions than about the tokenization process itself?
Because the tokenization process only has to work once, at issuance, while transfer restrictions have to work correctly for every subsequent transaction over the life of the asset. For regulated assets, that ongoing enforcement is what keeps the instrument compliant with securities law and offering terms after the initial sale.